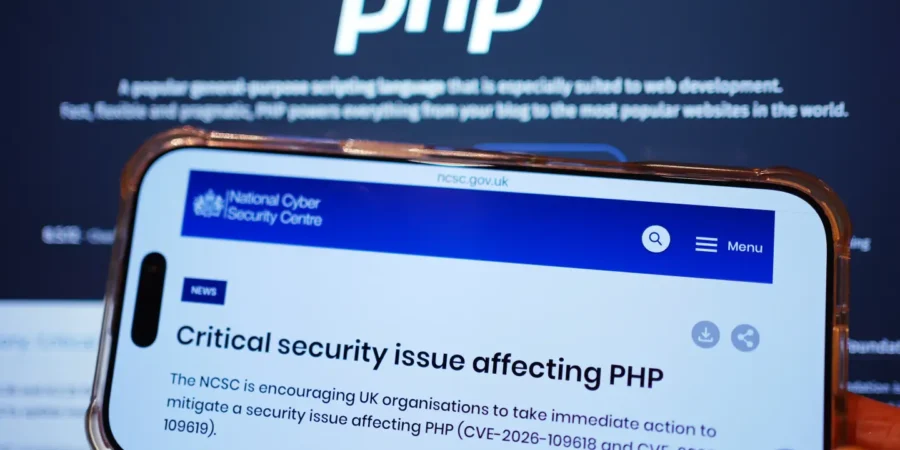
PHP security is currently in a post-crisis patching phase following the discovery of two critical vulnerabilities, collectively known as PHP2Shell, which were disclosed in late October 2026. These flaws, identified as CVE-2026-109618 and CVE-2026-109619, reside in PHP’s memory management and error handling systems, affecting nearly every web request on servers running the language since PHP 5.
The vulnerabilities were discovered by cybersecurity firms Wiz and Calif using OpenAI models, allowing attackers to execute unauthenticated remote code and take full control of web servers. The PHP Foundation released emergency patches on October 21, 2026, prompting global government agencies, including the NSA and CISA, to urge immediate updates.
While no major successful hacks have been widely confirmed, Cloudflare reported millions of exploitation attempts within hours of disclosure. Many organizations, particularly those running unsupported legacy versions, remain at high risk, leading to widespread precautionary website shutdowns and ongoing efforts to secure the estimated 70% of websites powered by PHP.
PHP remains a cornerstone of the modern web, powering roughly 75-76% of all websites with a known server-side programming language. However, its massive market share makes it a primary target for cyberattacks. The current situation of PHP in cybersecurity is a balancing act between modern security features introduced in PHP 8.x and legacy, poorly written codebases that remain highly vulnerable.
PHP Cybersecurity Matrix
| Vulnerability Type | Risk Level | Common Root Cause | Modern Mitigation Strategy |
|---|---|---|---|
| SQL Injection (SQLi) | High | Concatenating raw user input into SQL queries. | Use PDO or MySQLi with prepared statements. |
| Cross-Site Scripting (XSS) | High | Echoing unescaped user input into HTML templates. | Use htmlspecialchars() or modern template engines like Twig. |
| Remote Code Execution (RCE) | Critical | Using unsafe functions like eval() or unvalidated file uploads. | Disable dangerous functions in php.ini; strict file validation. |
| Insecure Deserialization | Medium | Passing untrusted data to unserialize(). | Use JSON format (json_encode/json_decode) instead. |
| Broken Authentication | High | Weak password hashing or poorly managed sessions. | Use password_hash() and enforce session.cookie_secure. |
10 Examples of PHP Security Best Practices & Vulnerabilities
- SQL Injection (Bad):
$db->query("SELECT * FROM users WHERE id = " . $_GET['id']); - SQL Injection (Good): Use
$stmt = $db->prepare('SELECT * FROM users WHERE id = ?'); $stmt->execute([$_GET['id']]); - XSS Protection: Always wrap dynamic output in HTML escaping:
echo htmlspecialchars($userInput, ENT_QUOTES, 'UTF-8'); - Secure Password Hashing: Never use MD5/SHA1. Use modern algorithms:
$hash = password_hash($password, PASSWORD_ARGON2ID); - Session Security: Prevent session hijacking by configuring your
php.iniwithsession.cookie_httponly = 1andsession.cookie_secure = 1. - File Upload Restriction: Restrict uploaded file types by checking MIME types and moving files outside the web root.
- Disabling Dangerous Functions: Block high-risk features in
php.iniusingdisable_functions = exec, passthru, shell_exec, system, eval. - Dependency Auditing: Regularly run
composer auditto scan third-party vendor packages for known vulnerabilities. - Error Management: Turn off public error reporting in production (
display_errors = Off) to prevent information disclosure. - Keeping PHP Updated: Upgrading to PHP 8.2 or 8.3 ensures active security patches; PHP 7.x and lower are officially End-of-Life (EOL) and insecure.
Psychological & Analytical Perspectives on PHP Security
To understand why PHP faces continuous security scrutiny, we can project the language’s architectural flaws and developer culture through the lenses of prominent analytical frameworks, theologians, and psychologists.
Myers-Briggs (MBTI) Analyst Report
- PHP Personality Profile: ESFP (The Performer)
- Analysis: PHP was built for immediate, practical output—getting things done quickly on the web. It is highly adaptable, spontaneous, and democratic. However, like an ESFP, it historically lacked long-term structured planning (Introverted Intuition) and rigorous internal logic (Introverted Thinking). This lack of strict discipline is exactly why security vulnerabilities thrive in PHP: it prioritizes convenience and rapid execution over rigorous structural safety.
Carl Jung Analyst Report
- The Archetype: The Trickster / The Shadow
- Analysis: PHP possesses a dual nature. Its conscious persona is the helpful, universal language of the internet. Its “Shadow” is the massive backlog of legacy PHP 4/5 codebases lurking in the dark corners of the web. The unconscious repetition of bad coding habits represents a structural “complex” within the developer community, where old vulnerabilities are repressed rather than fundamentally integrated and resolved through modern refactoring.
Jordan Peterson Analyst Report
- The Core Conflict: Order vs. Chaos
- Analysis: PHP represents a chaotic landscape of decentralized development. Anyone can write PHP, which democratizes the web but invites catastrophic chaos if standard protocols are ignored. A secure PHP application requires absolute discipline and adherence to strict, structured “rules of the game” (e.g., using frameworks like Laravel). Without a competent hierarchy of architectural design, the developer falls into the underworld of malicious exploitation.
John MacArthur Analyst Report
- Theological Parallel: The Fallibility of Man and Radical Depravity
- Analysis: PHP security flaws are a stark reminder of human fallibility. If you give a developer total freedom without strict constraints, their baseline nature will default to the easiest, most error-prone path. Security cannot rely on the “good intentions” of a coder; it requires an absolute, unyielding standard—a sovereign law (like strict typing and unalterable security frameworks)—to restrain the inherent mistakes of human logic.
Paul Washer Analyst Report
- Theological Parallel: Superficial Profession vs. Authentic Practice
- Analysis: Many claim to write secure PHP code simply because their application functions on the surface. But this is a superficial security. True security is narrow and difficult. It requires looking at the hidden, internal state of the application. If your codebase is filled with unexamined inputs and hidden dependencies, it is fundamentally broken, no matter how appealing the front-end user interface appears to the outside world.
Greg Schad Analyst Report
- Enterprise Infrastructure Perspective: Systems-Level Accountability
- Analysis: From an industrial operational standpoint, PHP’s security issues are rarely a failure of the language itself, but a failure of organizational systems. Legacy technical debt persists because management prioritizes feature deployment over infrastructure maintenance. To fix PHP security, an organization must implement rigorous continuous integration (CI/CD) pipelines, automated static analysis (like Psalm or Stan), and enforceable compliance metrics.
Note: We do use YouTube Video’s under the “Fair Use” Act under the Copyright Law:
“Fair use is a doctrine in the United States copyright law codified in Section 107 of the Copyright Act of 1976.1 It provides for the legal, non-licensed citation or incorporation of copyrighted material in another author’s work without requiring permission from the rights holders, such as for commentary, criticism, news reporting, research, teaching or scholarship.01 The U.S. Copyright Office Fair Use Index should prove helpful in understanding what courts have to date considered to be fair or not fair but it is not a substitute for legal advice.2“
Check out our last minute travel deals: Travelanycountry.com

Save Up To 60% Off Hotels, Flights, Cruises, Rental Cars More…
Product Reviews Ebay.com, Walmart.com, Clickbank, Cabela’s And More…
Women Product Reviews
- Women’s Handbags And Purses At Your Local Walmart Or Online Near Me!
- Women’s Clothes At Your Local Walmart Or Online Near Me!
- Kate Spade New York Women’s Carlyle Medium Shoulder Handbag – Black
- Kate Spade Leila Medium Gingerbread Leather Triple Compartment Satchel Handbag Product Review From Walmart
- MKF Collection Gabriella Handbag with Wallet by Mia K.
- MKF Collection Bonita Checkered Tote 2 Pcs Women’s Large Handbag with Wallet and Decorative M keychain by Mia k.
- Michael Kors 35H1T2Jt1C Jodie Small Logo Jacquard Tote Bag In Atom Green
- Michael Kors Gilly Drawstring Large Top Zip Tote Ballet Pink Mk Signature
- Michael Kors 35F1GTVT3B Jet Set Travel Large Chain Shoulder Tote Bag MK Signature Brown
Product Reviews – Apples Phones, TV, Ipads, Laptops, Watches
- Apple AirTag 4 Pack
- Apple AirPods Pro (2nd Generation) Wireless Earbuds, Up to 2X More Active Noise Cancelling, Adaptive Transparency, Personalized Spatial Audio, MagSafe Charging Case, Bluetooth Headphones for iPhone
- Apple Watch Series 3 GPS Silver – 42mm – White Sport Band
Product Reviews – Camera’s, Gimbal’s, Video Equipment.
Canon EOS M50 Mark II + EF-M 15-45mm is STM Kit Black Product Review
Other Product Reviews – Lawncare, Tools, Fishing Gear.
Troy-Bilt Pony 42″ Riding Lawn Mower Tractor with 42-Inch Deck and 439cc 17HP Troy-Bilt Engine
Costway 6.3 Quart Tilt-Head Food Stand Mixer 6 Speed 660W w/Dough Hook, Whisk Black
I COMPARE 4 RVs: Campervan, Class C, 5th Wheel & Truck Camper. 20 Factors to Consider
Offshore Angler Tightline II Spinning Reel
Lodge Tall Boy Camp Dutch Oven Tripod
Bear Archery Species EV RTH Compound Bow Package
Minn Kota Terrova Bow Mount Freshwater Trolling Motor with i-Pilot GPS Trolling System
Cabela’s Treadfast GORE-TEX Insulated Hunting Boots for Men
Classic Accessories Over Drive RV Sway Bar Hitch Tote, Black
Hughes Autoformers Power Watchdog Portable RV Bluetooth Surge Protector, 30 Amp
Black Max 21-inch 3-in-1 Self-Propelled Gas Mower with Perfect Pace Technology
Best Choice Products 6V Portable Sewing Machine, 42-Piece Beginners Kit w/ 12 Stitch Patterns – Teal
Please visit our Sponsors: