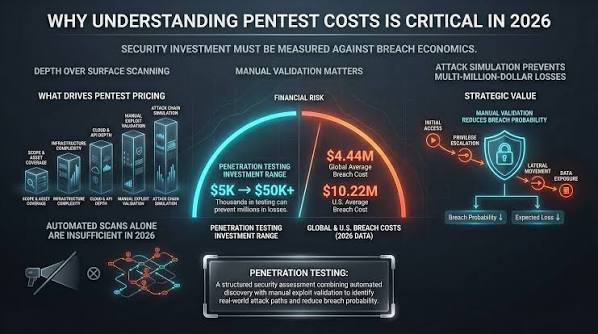
The economics of owning a penetration testing company are defined by high-margin, low-volume services driven by tester-days as the primary cost unit. A senior pen tester in the US or EU costs $1,200–$2,000 per day fully loaded, while juniors cost $400–$700, establishing the baseline for pricing tiers.
Pricing Tiers and Market Positioning
- Tier 1 ($1,500–$3,000): Automated scans with light human review; suitable for low-stakes compliance but lacks defensible security maturity evidence.
- Tier 2 ($4,000–$8,000): The “sweet spot” for SOC 2 readiness and enterprise hygiene, typically involving 5–15 tester-days of senior labor.
- Tier 3 ($10,000–$25,000): Required for complex environments like multi-tenant SaaS with sensitive data, where missed findings risk significant customer loss.
- Tier 4 ($30,000–$80,000+): Enterprise engagements from top firms involving multiple senior testers, dedicated project management, and full attack-tree development.
Operational Costs and Risks
- Fixed vs. Variable Costs: Successful firms often use fixed-fee pricing to avoid the unpredictability of hourly billing, though this requires accurate scoping to prevent margin erosion.
- Overhead and Liability: Owners must budget for professional liability insurance, which can range from $60,000 to $100,000 annually for high-limit policies (e.g., $30 million coverage).
- Quality vs. Cost: Cheap testing often relies on juniors or offshore labor, leading to false positives and remediation costs that can exceed the initial savings. The Return on Investment (ROI) for clients is often cited as 12,100%, based on the average data breach cost of $4.88 million versus a typical $40,000 test price for SMBs.
Strategic Considerations
- Scope Creep: Administrative overhead and unclear scoping can double costs; Penetration Testing as a Service (PTaaS) models help mitigate this by offering customizable, ongoing assessments.
- Vendor Reputation: Boutique firms may offer better quality-to-cost ratios than large generalist vendors, who might assign junior testers to large contracts.
- Hidden Costs: Buyers often overlook remediation retesting and administrative disruption to their staff, which can inflate the total cost of ownership beyond the initial quote.
What Does The KJV Bible Say?
Owning a penetration testing (pen testing) company is a unique economic venture. It combines technical asset evaluation, intense risk management, and the high-margin nature of specialized professional services.
Part 1: Financial & Biblical Foundations (KJV Framework)
The underlying financial mechanics of a modern cybersecurity consultancy map directly onto timeless principles of stewardship, assessment, and defense recorded in the King James Version (KJV) of the Bible.
Economic Ledger: KJV Principles applied to Cyber Business Operations
| Metric / Scenario | Financial Meaning | KJV Verse Citation | Biblical Wisdom Applied to Pen Testing |
|---|---|---|---|
| 1. Scoping / Cost Estimation | Calculating project scope and ensuring margin before deploying talent. | Luke 14:28 | “For which of you, intending to build a tower, sitteth not down first, and counteth the cost, whether he have sufficient to finish it?” |
| 2. Vulnerability Assessment | Proactively exposing network weak points before malicious actors strike. | Proverbs 27:23 | “Be thou diligent to know the state of thy flocks, and look well to thy herds.” |
| 3. Risk Remediation | Fixing structural flaws discovered during the test. | Ezekiel 13:5 | “Ye have not gone up into the gaps, neither made up the hedge for the house of Israel to stand in the battle in the day of the Lord.” |
| 4. Zero-Trust Architecture | Verifying access; assuming any human actor could introduce risk. | Jeremiah 17:5 | “Thus saith the Lord; Cursed be the man that trusteth in man, and maketh flesh his arm, and whose heart departeth from the Lord.” |
| 5. Defense-in-Depth | Implementing multiple layers of logical security barriers. | Ecclesiastes 4:12 | “And if one prevail against him, two shall withstand him; and a threefold cord is not quickly broken.” |
| 6. The Malicious Threat Actor | Understanding the persistent threat of hackers seeking unpatched entry. | 1 Peter 5:8 | “Be sober, be vigilant; because your adversary the devil, as a roaring lion, walketh about, seeking whom he may devour.” |
| 7. Talent Acquisition Cost | Investing heavily in rare, elite ethical hackers to protect assets. | Luke 10:7 | “…for the labourer is worthy of his hire. Go not from house to house.” |
| 8. Legal & Compliance SOW | Executing ironclad Statements of Work to prevent rogue testing liabilities. | Romans 13:7 | “Render therefore to all their dues: tribute to whom tribute is due; custom to whom custom; fear to whom fear; honour to whom honour.” |
| 9. Red Teaming Operations | Secretly assessing defensive readiness to catch teams off-guard. | Proverbs 25:9 | “Debate thy cause with thy neighbour himself; and discover not a secret to another.” |
| 10. Post-Engagement Reporting | Providing a transparent, accurate report of flaws without falsifying data. | Proverbs 11:1 | “A false balance is abomination to the Lord: but a just weight is his delight.” |
Part 2: Thinker & Analyst Reports
Myers-Briggs Type Indicator (MBTI) Analyst Report
- Corporate Persona: INTJ (The Mastermind) & INTP (The Logician).
- The Economic Diagnosis: The pen testing model excels due to structural introverted intuition and thinking. It relies heavily on asymmetric knowledge—the firm monetizes what clients cannot see. However, the economic bottleneck is scaling. The business model inherently resists democratization because it depends on quirky, highly analytical talent pools who prefer solving puzzles over structured corporate processes. To maximize profitability, the firm must carefully transition from custom manual labor to scalable productized services (automated scanning modules), bridging the gap between introverted analytical depth and extroverted market demands.
John MacArthur Analyst Report
- Corporate Persona: Biblical Expositor & Sovereign Institutionalist.
- The Economic Diagnosis: A pen testing firm must operate with unyielding, objective truth. A report that sugarcoats a vulnerability to please a client is a moral failure and a breach of stewardship. The economics of the firm should be built on absolute integrity—no inflated hours, no hidden fees, and zero tolerance for rogue, unauthorized hacking. The firm’s primary economic value is exposure of reality; it serves a sovereign purpose by cutting through institutional pride and exposing the fragile, fallible state of human-made digital empires.
Paul Washer Analyst Report
- Corporate Persona: Radical Reformed Apologist.
- The Economic Diagnosis: This enterprise exists because the human heart is radically depraved, deceitful, and desperately wicked. If there were no thieves, malicious actors, or digital predators, this industry would have an economic value of zero. Therefore, a pen testing company must never become proud of its revenues. The profits generated are a somber reminder of a broken world. The firm must operate with extreme sobriety, realizing that security is an illusion and that relying on technology alone to save an enterprise from ruin is a form of idolatry.
Greg Schad Analyst Report
- Corporate Persona: Enterprise Cybersecurity Executive & AppSec Pragmatist.
- The Economic Diagnosis: Traditional point-in-time pen testing is a flawed economic model for modern enterprises. Security teams are shipping code faster than ever. A annual or quarterly manual pen test provides a reactive stamp of approval that is obsolete the moment a new deployment occurs. To achieve highly sustainable operating margins, companies must shift from purely reactive “checking the box” consulting to proactive, continuous application security and software supply chain protection. The highest lifetime value (LTV) clients are those integrated into continuous threat modeling and proactive defense structures.
Jordan Peterson Analyst Report
- Corporate Persona: Clinical Archetypal Pragmatist.
- The Economic Diagnosis: Look, a pen testing company is essentially an institutionalized encounter with the dragon of chaos. If you don’t voluntarily invite ethical hackers to find the cracks in your castle wall, the catastrophic force of an actual malicious breach will inevitably manifest and destroy your hierarchy. Economically, firms that fail to integrate pen testing are acting out a blind, ideological delusion of competence. The business owner is selling voluntary, controlled exposure to danger, which is the only known psychological and organizational mechanism for developing true competence and resilience.
Carl Jung Analyst Report
- Corporate Persona: Psychoanalytic Depth Psychologist.
- The Economic Diagnosis: The pen testing firm acts as the collective “Shadow” integration mechanism for the corporate psyche. Every enterprise projects an external persona of flawless security, compliance, and absolute control. Beneath this mask lies the repressed shadow—unpatched software, legacy infrastructure, and human vulnerability. The economics of the pen testing business rely on bringing this digital unconscious into conscious awareness. The firm’s high margins are a psychological tax that corporations pay to avoid a catastrophic, disruptive eruption of their unaddressed shadows.
6 Month Game Plan, Business Plan, Marketing Plan
6-Month Execution Framework
       MONTH 1-2                    MONTH 3-4                    MONTH 5-6
+-----------------------+    +-----------------------+    +-----------------------+

|  Foundation & Assets  |    |  Pipeline Acceleration|    |   Scale & Productize  |
|                       |    |                       |    |                       |
| • Corporate Setup     |    | • Outbound Campaigns  |    | • Mid-Market Engine   |
| • Legal SOW Framework | -> | • Strategic Joint VTs | -> | • Productized Scope   |
| • Initial Tech Stack  |    | • Proof of Concept V1 |    | • Retainer Engine V1  |
+-----------------------+    +-----------------------+    +-----------------------+
Part 1: 6-Month Tactical Game Plan
Month 1–2: Infrastructure & Legal Shielding
- Establish Business Entities: Register an LLC or C-Corp using local corporate structures; acquire a minimum of $2M/$4M Professional Liability (Errors & Omissions) and Cyber Liability insurance policies immediately.
- Draft Legal SOW & Rules of Engagement (ROE): Retain a specialized technology attorney to draft a standard Statement of Work (SOW), Master Services Agreement (MSA), and an ironclad Rules of Engagement document. The ROE must require explicit, written, cryptographic authorization from the asset owner before a single packet is sent. This fulfills the mandate of Romans 13:7 (“Render therefore to all their dues…”) by ensuring absolute boundary clarity.
- Provision the Technical Operations Stack: Deploy a secure, isolated Command and Control (C2) infrastructure using dedicated virtual private servers (VPS). Set up encrypted reporting pipelines and secure asset storage repositories (e.g., self-hosted, air-gapped, or highly restricted cloud enclaves) to protect sensitive client vulnerability data discovered during testing (Proverbs 27:23).
Month 3–4: Market Validation & Direct Outreach
- Launch Target Profiling Engines: Assemble a localized account list targeting mid-market enterprises across highly regulated verticals (Healthcare/HIPAA, Financials/PCI-DSS, Defense Logistics/CMMC).
- Execute Cold-Outbound Sequences: Initiate value-first outbound prospecting campaigns targeting Chief Information Security Officers (CISOs) and VPs of Infrastructure. Offer a complimentary external perimeter asset-discovery scan to expose unpatched or forgotten public-facing infrastructure. This controlled encounter brings hidden risks to light, serving as a tactical implementation of the Jordan Peterson and Carl Jung “Shadow Integration” frameworks.
- Secure Pilot Projects: Close 3 initial Proof-of-Concept (PoC) or subsidized manual engagements. Use these initial operations to stress-test your team’s internal delivery timelines, testing methodologies, and report generation workflows.
Month 5–6: Optimization & Retainer Scaling
- Standardize the Delivery Engine: Convert manual findings into a high-fidelity, reproducible remediation report format matching the objective standards of Proverbs 11:1 (“a just weight is his delight”). Deliver clean executive summaries alongside clear, actionable developer-focused remediation steps.
- Upsell to Continuous Security Models: Transition early point-in-time test clients into continuous application security or quarterly threat-modeling retainers. This addresses the core critique in the Greg Schad Analyst Report by converting erratic project-based revenue into predictable Monthly Recurring Revenue (MRR).
- Expand Technical Delivery Team: Hire your first dedicated contract or full-time Offensive Security Certified Professional (OSCP) to offload manual execution from the founder, preserving enterprise margins for strategic business growth.
Part 2: Concrete Business Plan
1. Executive Summary
The company provides premium offensive security, penetration testing, and continuous vulnerability assessment services. By combining elite, manual human intuition with rigorous compliance mapping, the firm systematically uncovers structural digital flaws before malicious actors can exploit them (1 Peter 5:8). The enterprise operates as a high-margin professional services firm with a deliberate roadmap to productize its delivery model.
2. Financial Plan & Operating Metrics
The business targets an initial 70% Gross Margin on purely manual consulting delivery.
AI-generated. Don’t enter sensitive personal info.
- Initial Capitalization: $15,000 baseline budget for infrastructure, licensing, legal setup, and corporate insurance.
- Pricing Architecture:
- Mid-Market External/Internal Network Test: $12,000–$20,000 per engagement (Fixed Scope).
- Web/Mobile Application Security Testing: $15,000–$30,000 depending on API density and user roles (Luke 14:28).
- Continuous Security Advisory Retainer: $3,500–$7,500/month (Requires a 12-month minimum commitment).
3. Human Capital & Talent Optimization
- Elite Labor Costs: Ethical hacking talent is rare and commands premium compensation (Luke 10:7). The business utilizes a fractional contractor model for the first 4 months to align labor expenses directly with contract revenues.
- Core Skillsets: The technical team must maintain active tier-one certifications (OSCP, OSWE, GXPN) and demonstrate strict compliance with absolute disclosure integrity (John MacArthur Report).
Part 3: Strategic Marketing Plan
1. Core Positioning Strategy
The company rejects generic, automated automated-scanning checklists. Our core value proposition centers on Rigorous, Human-Led Reality Assessments. We frame cybersecurity not as a fear-based liability, but as a discipline of competitive resilience, business continuity, and structural truth.
2. Growth & Client Acquisition Channels
Account-Based Marketing (ABM) for Regulated Verticals
- Action: Direct mail combined with multi-channel digital outreach targeting compliance officers at regional banks and healthcare networks.
- Asset: Provide a physical, printed copy of a sanitized, redacted, highly detailed Pen Test Report to visually demonstrate the depth of our elite manual analysis over standard automated printouts.
Strategic Channel Partnerships
- Action: Partner with local Managed Service Providers (MSPs) and Virtual CISOs (vCISOs).
- Value Exchange: MSPs are contractually and ethically prohibited from auditing their own work. By functioning as an independent, third-party assessment firm, we provide an objective validation layer that strengthens their client relationships without creating a conflict of interest (Ecclesiastes 4:12).
Truth-Driven Technical Content Architecture
- Action: Publish deep-dive technical breakdowns of real-world software supply chain vulnerabilities, zero-day threat landscapes, and active remediation strategies.
- Tone: Objective, authoritative, and completely devoid of traditional marketing fluff or hyperbole. This approach aligns directly with the analytical clarity required by the Myers-Briggs (INTJ/INTP) and Paul Washer operational assessments.
First 10 People To Hirer In Order?
To build a highly profitable, legally bulletproof penetration testing firm, your hiring sequence must carefully balance revenue generation, elite technical delivery, and risk management.
The following 10-person hiring blueprint scales your business from a founder-led consultancy to an enterprise-grade offensive security firm.
Phase 1: The Foundation & Delivery Engine (Employees 1–3)
This phase transitions the founder out of acting as the sole technical delivery mechanism, creating a repeatable delivery machine.
- 1. Senior Penetration Tester / Technical Lead (OSCP / OSCE / GXPN)
- Why first: You cannot scale if the founder is spending 40 hours a week running exploits and writing 80-page reports. This individual owns the technical execution of your core network and web application tests, fulfilling Luke 10:7 (“the labourer is worthy of his hire”).
- Key trait: Strong consulting skills; they must be able to present findings directly to a client’s technical staff without causing defensive friction.
- 2. Account Executive / Head of Business Development
- Why second: To feed your newly hired Senior Tester, you need a dedicated engine focused on cold outbound outreach, account-based marketing, and MSP channel partnerships.
- Key trait: Experience selling high-ticket technical services ($15k–$100k contracts) to CISOs and VPs of Infrastructure, not just selling software licenses.
- 3. Mid-Level Security Consultant (OSCP)
- Why third: To protect your margins. A senior tester’s time shouldn’t be consumed by standard external scanning, asset discovery, or foundational report formatting. The mid-level tester executes the core blocking-and-tackling while learning advanced exploitation from the Senior Lead.
Phase 2: Operations & Specialized Expansion (Employees 4–6)
This phase introduces structural efficiency, project management, and high-margin specialized service offerings.
- 4. Project Manager / Technical Operations Coordinator
- Why fourth: Pen testing logistics are complex. They require scheduling around client maintenance windows, managing Rules of Engagement (ROE) sign-offs, tracking milestones, and delivering reports on time. A dedicated PM keeps your testers billing hours and prevents operational chaos (Luke 14:28).
- Key trait: Absolute organizational discipline; background in technical project management (Agile/Scrum).
- 5. Senior Application Security (AppSec) Specialist (OSWE / CASE)
- Why fifth: To capture the high-margin market highlighted in the Greg Schad Analyst Report. As enterprises move away from annual infrastructure tests toward continuous code deployment, an elite AppSec engineer allows you to sell secure code reviews, API assessments, and DevSecOps pipeline integrations.
- 6. Red Team Operations Lead (CRTO / SE-Certified)
- Why sixth: This role moves your firm beyond standard compliance testing into advanced adversary simulation (Proverbs 25:9). The Red Team Lead designs custom physical, social engineering, and multi-layered logical attack campaigns to test an enterprise’s actual incident response capabilities (the Jordan Peterson Chaos Integration).
Phase 3: Corporate Scale & Quality Control (Employees 7–10)
This phase hardens your internal infrastructure, protects against legal liabilities, and institutionalizes the sales cycle.
- 7. Internal Security & Infrastructure Engineer (DevSecOps / SysAdmin)
- Why seventh: As a pen testing firm, you are a high-value target. You store client vulnerability data, custom exploits, and access credentials. You need a dedicated resource to manage your isolated command-and-control (C2) servers, implement zero-trust access controls, and defend your own perimeter (Proverbs 27:23).
- 8. Quality Assurance (QA) Specialist & Technical Writer
- Why eighth: The ultimate product of a pen test is the report. If a report contains typos, poor formatting, or weak remediation advice, the perceived value drops to zero (Proverbs 11:1). A technical editor ensures every deliverable matches a flawless, executive-ready standard.
- 9. Second Senior Penetration Tester (Enterprise Specialist)
- Why ninth: To handle the parallel execution of multiple large enterprise accounts, preventing delivery bottlenecks and allowing the original Tech Lead to step into a true Chief Technology Officer (CTO) framework.
- 10. Director of Marketing / Growth Marketing Manager
- Why tenth: Once your delivery engine, sales processes, and QA framework are fully institutionalized, you inject capital into a true inbound marketing engine. They build your authority via truth-driven technical whitepapers, zero-day threat analysis distribution, and targeted regional cybersecurity events.
Summary Table: Financial & Functional Alignment
| Hire Order | Role | Primary Economic Value | Core Metric |
|---|---|---|---|
| 1 | Senior Pen Tester | Delivers current projects; frees founder time. | Billable Utilization Rate |
| 2 | Account Executive | Populates pipeline; drives new contract revenue. | Customer Acquisition Cost (CAC) / Pipeline Value |
| 3 | Mid-Level Tester | Maximizes project gross margin via labor leverage. | Cost per Deliverable |
| 4 | Project Manager | Streamlines delivery schedules; avoids scope creep. | Project Profitability / On-Time Delivery Rate |
| 5 | AppSec Specialist | Opens high-ticket continuous software security lines. | Average Contract Value (ACV) Extension |
| 6 | Red Team Lead | Up-sells mid-market clients into premium engagements. | Retainer Conversion Percentage |
| 7 | Infrastructure Eng | Mitigates enterprise operational and security risk. | Zero Internal Breaches / System Uptime |
| 8 | QA / Tech Writer | Drives client satisfaction and retention through clarity. | Client Renewal Rate |
| 9 | Senior Tester #2 | Expands capacity for simultaneous concurrent projects. | Firm Gross Capacity (USD) |
| 10 | Marketing Director | Builds automated inbound lead generation engine. | Marketing Qualified Leads (MQL) per Month |
Should we hire these individuals as W2 full-time employees from day one, or start them as fractional 1099 contractors?
To optimize your cash flow and protect your business from structural risk, you should use a hybrid approach: start your technical delivery team as fractional 1099 contractors, but place your client-facing sales engine on a W2 framework early.
This strategy prevents you from taking on massive, fixed monthly payroll obligations before your contract pipeline is completely predictable, aligning directly with the cautious planning mandated in Luke 14:28 (“counteth the cost”).
The Economic & Structural Trade-offs
                  1099 CONTRACTOR                   W2 FULL-TIME EMPLOYEE
          +------------------------------+  +------------------------------+
   PROS:  | • Zero fixed payroll risk    |  | • Absolute operational control|

          | • Aligns cost with contract  |  | • Rigid IP protection        |
          | • No benefit overhead burden |  | • High long-term loyalty     |
          +------------------------------+  +------------------------------+
   CONS:  | • Loose scheduling control   |  | • High fixed overhead burden |

          | • Compliance reclassification|  | • Must pay if pipeline drops |
          +------------------------------+  +------------------------------+
The Strategic Recommendation Matrix
1. Technical Delivery Team (Hires 1, 3, 5, 6)
- The Verdict: Start as 1099 Contractors, migrate to W2 at a clear revenue trigger.
- The Rationale: Elite testers are expensive. Paying a full-time W2 Senior Tester $140k–$180k+ base salary when you only have two active projects will drain your cash reserves. By utilizing 1099 structures, you pay them an agreed-upon hourly or per-project rate only when a client is actively paying you.
- The Trigger to W2: Move a contractor to a full-time W2 role once their individual billable project pipeline consistently hits 30 hours per week for 3 consecutive months.
2. Sales & Business Development (Hire 2)
- The Verdict: Hire as W2 from Day One (Base + Commission).
- The Rationale: You cannot build a predictable, repeatable pipeline with a fractional 1099 sales rep who is simultaneously pitching services for three other companies. To build an enterprise pipeline, you need absolute focus and accountability.
- The Legal Layer: Under U.S. IRS guidelines, if you direct an individual’s daily activity, specify their work hours, and require them to use your corporate CRM and email, they are legally a W2 employee. Misclassifying a full-time sales rep as a 1099 contractor carries steep legal and financial penalties.
3. Operational & Support Roles (Hires 4, 7, 8, 10)
- The Verdict: Utilize fractional 1099 or specialized agency partnerships initially.
- The Rationale: Project management, infrastructure maintenance, and report quality assurance do not require 40 hours of operational capacity per week during your first 6 months. Retaining a fractional Project Manager for 10 hours a week protects your operating margins while maintaining institutional organization (Proverbs 11:1).
Critical Risk Factors & The “Hidden Costs”
The Intellectual Property (IP) Shield
When a 1099 contractor writes custom exploit code or creates a proprietary pen testing report template for your firm, they technically own that intellectual property by default unless a specialized agreement is executed.
- The Fix: Every 1099 contract must include an explicit, ironclad “Work Made For Hire” provision and a robust Non-Disclosure Agreement (NDA). This ensures your firm retains exclusive ownership of all discovered vulnerabilities and custom tooling, reflecting the security caution found in Proverbs 27:23.
IRS Reclassification Risk
The IRS aggressively audits firms that treat workers like full-time employees but label them as 1099 contractors to avoid payroll taxes and benefits.
- The Rule: Your 1099 testers must have control over how and when they perform the work, use their own primary testing hardware (unless client security compliance mandates using an isolated corporate virtual machine), and have the freedom to work with other non-competing clients.
Summary Checklist for Implementation
- Draft two separate legal onboarding packages: One for 1099 Master Services Agreements (with strict Work-Made-For-Hire clauses) and one for standard W2 employment.
- Incorporate a 15%–25% tax/benefit overhead burden into your financial model for every role you plan to transition from 1099 to W2.
- Establish clear, objective milestone triggers in your business plan so your team knows exactly when contract work will evolve into a stable, full-time position.
What are the legal risks of penetration testing?
Penetration testing is unique because the technical acts performed—unauthorized access, executing exploits, intercepting traffic, and bypassing security controls—are highly illegal computer crimes unless backed by explicit, valid legal authorization. Without precise legal scaffolding, an ethical hacker can face severe civil lawsuits or felony criminal prosecution under federal, state, and international laws.
The primary legal risks and the frameworks used to mitigate them include the following:
1. Primary Statutory Risks (The Legal Landmines)
The Computer Fraud and Abuse Act (CFAA) – 18 U.S.C. § 1030
- The Risk: This is the primary federal anti-hacking statute in the United States. It criminalizes accessing a “protected computer” without authorization or exceeding authorized access.
- The Reality: If your tester targets an IP address, domain, or cloud bucket that turns out to be outside the agreed-upon scope, you have accessed a machine “without authorization.” Under the CFAA, this can be prosecuted as a federal felony, regardless of your intent to help.
The Wiretap Act & Electronic Communications Privacy Act (ECPA)
- The Risk: These laws govern the interception of wire, oral, or electronic communications.
- The Reality: If a pen tester performs a Man-in-the-Middle (MitM) attack, sniffs unencrypted network traffic, or captures cleartext employee credentials in transit, they may be violating wiretapping laws unless all parties (or the corporate entity owning the network) have explicitly consented to the interception.
State and Local Computer Crime Statutes
- The Risk: Every U.S. state has its own version of computer crime laws (e.g., California’s Comprehensive Computer Data Access and Fraud Act).
- The Reality: State laws can sometimes be more rigid than federal statutes, allowing local law enforcement or state prosecutors to pursue charges for localized computer trespass, even if federal authorities decline to prosecute.
2. Operational & Contractual Risks
Scope Creep and Shared/Cloud Infrastructure
- The Shared-Fate Problem: Most modern businesses run on cloud infrastructure (AWS, Azure, Google Cloud) or use third-party SaaS products.
- The Legal Trap: A client can only authorize you to test assets they actually own. If your tester targets a client’s server and inadvertently disrupts the underlying AWS physical host, or attacks a third-party API integrated into the client’s app, you are attacking a third party’s property without their consent. AWS or the third-party provider can pursue legal action against your firm.
Data Breaches & Exfiltration of Regulated Data
- The Risk: During a test, your team may successfully breach a database containing sensitive personal data (PII, PHI, or PCI data).
- The Legal Trap: If your tester downloads this data to your local testing machine to prove the vulnerability, your firm is now legally holding unencrypted regulated data. If your firm’s testing infrastructure is breached, or if a disgruntled contractor leaks it, you are liable for the data breach. This violates the absolute stewardship metrics outlined in Proverbs 27:23.
System Downtime and Business Interruption (Civil Liability)
- The Risk: Running a heavy vulnerability scan or executing an exploit can accidentally crash a production database, corrupt a file system, or take down an e-commerce storefront.
- The Legal Trap: The client can sue your firm for lost revenue, data recovery costs, and punitive damages, claiming professional negligence or breach of contract.
3. Critical Mitigations: The Legal Shield
To operate safely, a pen testing company must establish an ironclad legal barrier before a single packet is sent. This directly mirrors the wisdom of Luke 14:28 by calculating the operational risk before building the enterprise.
       MASTER SERVICES AGREEMENT (MSA)
       • Establishes general business relationship, fees, & broad liabilities.
                      │
                      ▼
          STATEMENT OF WORK (SOW)
       • Defines exact project timelines, costs, and deliverables.
                      │
                      ▼
       RULES OF ENGAGEMENT (ROE) & "GET OUT OF JAIL FREE" CARD
       • Explicit IP/Domain boundaries, allowed methods, & explicit owner consent.
The Master Services Agreement (MSA) & Statement of Work (SOW)
- Limitation of Liability (LoL): Your contract must cap your maximum liability at the amount paid for the specific engagement (or a reasonable multiple of it) to protect your company from business-ending lawsuits if an accidental system crash occurs.
- Mutual Indemnification: The client must indemnify and hold your firm harmless against any third-party claims (like AWS or SaaS providers) arising from your testing of the systems the client directed you to test.
The Rules of Engagement (ROE) Document
This is your primary legal shield. It must be written, explicit, and cryptographically or physically signed by an officer of the client company who has the actual authority to grant access to the networks (Romans 13:7).
- White-Listed Targets: A definitive list of exact IP addresses, fully qualified domain names (FQDNs), and API endpoints. If it is not on the list, it is strictly off-limits.
- Explicit Restrictions: Clearly outline what is prohibited (e.g., “No Denial of Service (DoS) attacks,” “No social engineering of low-level helpdesk employees,” “Testing only between 12:00 AM and 4:00 AM EST”).
- The “Get Out of Jail Free” Letter: Provide your active testers with a formal authorization letter signed by the client’s executive sponsor. It must state their names, the exact dates of the test, and a 24/7 corporate emergency phone number. If a physical or remote red teamer is caught by internal IT or law enforcement, this letter is their immediate verification mechanism (Proverbs 25:9).
How do international laws differ from the CFAA?
While the U.S. Computer Fraud and Abuse Act (CFAA) focuses heavily on the binary concept of technical boundaries (whether a tester bypassed a digital gate), international cyber laws often introduce much more rigid restrictions. For a globally operating penetration testing company, what is legal under the CFAA can easily be classified as a severe criminal offense overseas.
The structural legal differences that separate the CFAA from global frameworks include the following:
1. Intent vs. Pure Access (The Threshold of a Crime)
- The CFAA Standard: Following the landmark 2021 Supreme Court ruling in Van Buren v. United States, the CFAA focuses tightly on a code-based or technical barrier approach. If you have authorized access to a specific database folder, misusing that data for an unauthorized purpose does not automatically trigger a federal CFAA hacking violation. Furthermore, the U.S. Department of Justice explicitly exempts “good-faith” security research from prosecution under its internal guidelines.
- The International Difference: Many countries maintain a blanket approach to unauthorized access. In the United Kingdom, the Computer Misuse Act 1990 (CMA) makes any unauthorized access a strict liability crime under Section 1, regardless of your ultimate intent, ethical research goals, or whether you bypassed a technical barrier.
2. Dual-Use Tools & Possession Laws
- The CFAA Standard: In the United States, merely possessing, downloading, or writing common pen testing tools (e.g., Metasploit, Nmap, Burp Suite) is entirely legal. The crime occurs only when those tools are deployed maliciously to access a system without authorization.
- The International Difference: Several international frameworks criminalize the mere development, possession, or distribution of hacking software.
- United Kingdom (CMA Section 3A): It is an offense to make, supply, or obtain an article intending it to be used to commit a computer misuse offense.
- Germany (StGB § 202c – “The Hacker Paragraph”): Germany’s implementation of EU cybercrime directives explicitly criminalizes the preparation of a data espionage offense by producing, selling, or obtaining software intended for hacking. For German-based testers, configuring certain offensive exploits or automated scanning tools outside a strictly verified, air-gapped lab environment introduces severe exposure to domestic criminal prosecution.
3. Data Protection as a Companion Crime
- The CFAA Standard: The CFAA is purely an anti-hacking statute. If you accidentally pull a database containing customer records during a test, you are evaluated primarily on whether your access crossed into an unauthorized zone.
- The International Difference: In the European Union, cyber security testing is governed tightly by the General Data Protection Regulation (GDPR) alongside national hacking laws. Under GDPR Article 32, a company must perform security assessments. However, if an external pen tester accidentally exfiltrates or handles European citizens’ Personal Identifiable Information (PII) without a specialized, pre-approved Data Processing Agreement (DPA), both the testing firm and the client face crushing regulatory fines for data protection violations. The lack of a malicious breakthrough does not shield you from regulatory penalties.
4. Cross-Border Enforcement Frameworks
   BUDAPEST CONVENTION (Council of Europe)       UN CYBERCRIME CONVENTION (Hanoi)
+------------------------------------------+  +------------------------------------------+

| • Standardized cyber offenses across     |  | • Expands evidence sharing powers to     |
|   80+ allied nations.      |  |   ANY serious global crime.       |
| • Focuses on defined digital hacking     |  | • Opposed by US/allies over weak civil   |
|   boundaries and protections.    |  |   liberty and privacy safeguards.|
+------------------------------------------+  +------------------------------------------+
- The Budapest Convention on Cybercrime: This treaty functions as a global baseline for local cyber legislation across more than 80 aligned nations (including the US, UK, Japan, and EU members). It provides a standardized framework for sharing electronic evidence and enforcing cross-border tracking when a tester in one member nation accidentally compromises infrastructure in another.
- The U.N. Cybercrime Convention (Hanoi): Adopted by the UN General Assembly, this treaty expands cooperation powers to share electronic data across a broader, state-centric group of nations (including Russia and China). The U.S. and its core Western allies delayed or abstained from signing this protocol due to serious concerns over a lack of human rights safeguards, warning that its broad reach could allow authoritarian regimes to request data on independent global security researchers under the guise of an “unauthorized access” investigation.
Strategic Takeaway for the Business Owner
If your business is located in the U.S. but your team targets systems hosted in European cloud regions, or if you execute scans that touch international nodes, you must ensure your Rules of Engagement (ROE) document lists the exact geographical hosting locations of the assets. You must verify that your Statement of Work incorporates the explicit data protection mandates of the target jurisdiction.
Note: We do use YouTube Video’s under the “Fair Use” Act under the Copyright Law:
“Fair use is a doctrine in the United States copyright law codified in Section 107 of the Copyright Act of 1976.1 It provides for the legal, non-licensed citation or incorporation of copyrighted material in another author’s work without requiring permission from the rights holders, such as for commentary, criticism, news reporting, research, teaching or scholarship.01 The U.S. Copyright Office Fair Use Index should prove helpful in understanding what courts have to date considered to be fair or not fair but it is not a substitute for legal advice.2“
Check out our last minute travel deals: Travelanycountry.com

Save Up To 60% Off Hotels, Flights, Cruises, Rental Cars More…
Product Reviews Ebay.com, Walmart.com, Clickbank, Cabela’s And More…
Women Product Reviews
- Women’s Handbags And Purses At Your Local Walmart Or Online Near Me!
- Women’s Clothes At Your Local Walmart Or Online Near Me!
- Kate Spade New York Women’s Carlyle Medium Shoulder Handbag – Black
- Kate Spade Leila Medium Gingerbread Leather Triple Compartment Satchel Handbag Product Review From Walmart
- MKF Collection Gabriella Handbag with Wallet by Mia K.
- MKF Collection Bonita Checkered Tote 2 Pcs Women’s Large Handbag with Wallet and Decorative M keychain by Mia k.
- Michael Kors 35H1T2Jt1C Jodie Small Logo Jacquard Tote Bag In Atom Green
- Michael Kors Gilly Drawstring Large Top Zip Tote Ballet Pink Mk Signature
- Michael Kors 35F1GTVT3B Jet Set Travel Large Chain Shoulder Tote Bag MK Signature Brown
Product Reviews – Apples Phones, TV, Ipads, Laptops, Watches
- Apple AirTag 4 Pack
- Apple AirPods Pro (2nd Generation) Wireless Earbuds, Up to 2X More Active Noise Cancelling, Adaptive Transparency, Personalized Spatial Audio, MagSafe Charging Case, Bluetooth Headphones for iPhone
- Apple Watch Series 3 GPS Silver – 42mm – White Sport Band
Product Reviews – Camera’s, Gimbal’s, Video Equipment.
Canon EOS M50 Mark II + EF-M 15-45mm is STM Kit Black Product Review
Other Product Reviews – Lawncare, Tools, Fishing Gear.
Troy-Bilt Pony 42″ Riding Lawn Mower Tractor with 42-Inch Deck and 439cc 17HP Troy-Bilt Engine
Costway 6.3 Quart Tilt-Head Food Stand Mixer 6 Speed 660W w/Dough Hook, Whisk Black
I COMPARE 4 RVs: Campervan, Class C, 5th Wheel & Truck Camper. 20 Factors to Consider
Offshore Angler Tightline II Spinning Reel
Lodge Tall Boy Camp Dutch Oven Tripod
Bear Archery Species EV RTH Compound Bow Package
Minn Kota Terrova Bow Mount Freshwater Trolling Motor with i-Pilot GPS Trolling System
Cabela’s Treadfast GORE-TEX Insulated Hunting Boots for Men
Classic Accessories Over Drive RV Sway Bar Hitch Tote, Black
Hughes Autoformers Power Watchdog Portable RV Bluetooth Surge Protector, 30 Amp
Black Max 21-inch 3-in-1 Self-Propelled Gas Mower with Perfect Pace Technology
Best Choice Products 6V Portable Sewing Machine, 42-Piece Beginners Kit w/ 12 Stitch Patterns – Teal
Please visit our Sponsors: